Updated November 2, 2026
Centralized exchanges hold billions of dollars in customer assets, making them prime targets in crypto. The 10 largest centralized exchange (CEX) hacks on record have now resulted in more than $10B in losses combined, and two of them occurred in the past six weeks.
In this updated edition of our most-read blog, we rank the 10 biggest CEX hacks in history, from the $196M BitMartbreach in December 2021 to Binance’s record loss on October 29, 2026. All figures show the US dollar value at the time of the theft,updated where necessary, and focus only on CEX events (hence the absence of hacks such as Ronin, Poly Network, and Wormhole from this list). For each hack, we explain what happened, how the attackers got in, and what it means for compliance and security teams.
Two trends run through the list. Most attacks targeted the wallets exchanges use to move funds, or the systems that sign for them. And North Korean groups are confirmed or suspected in six of the 10 cases.
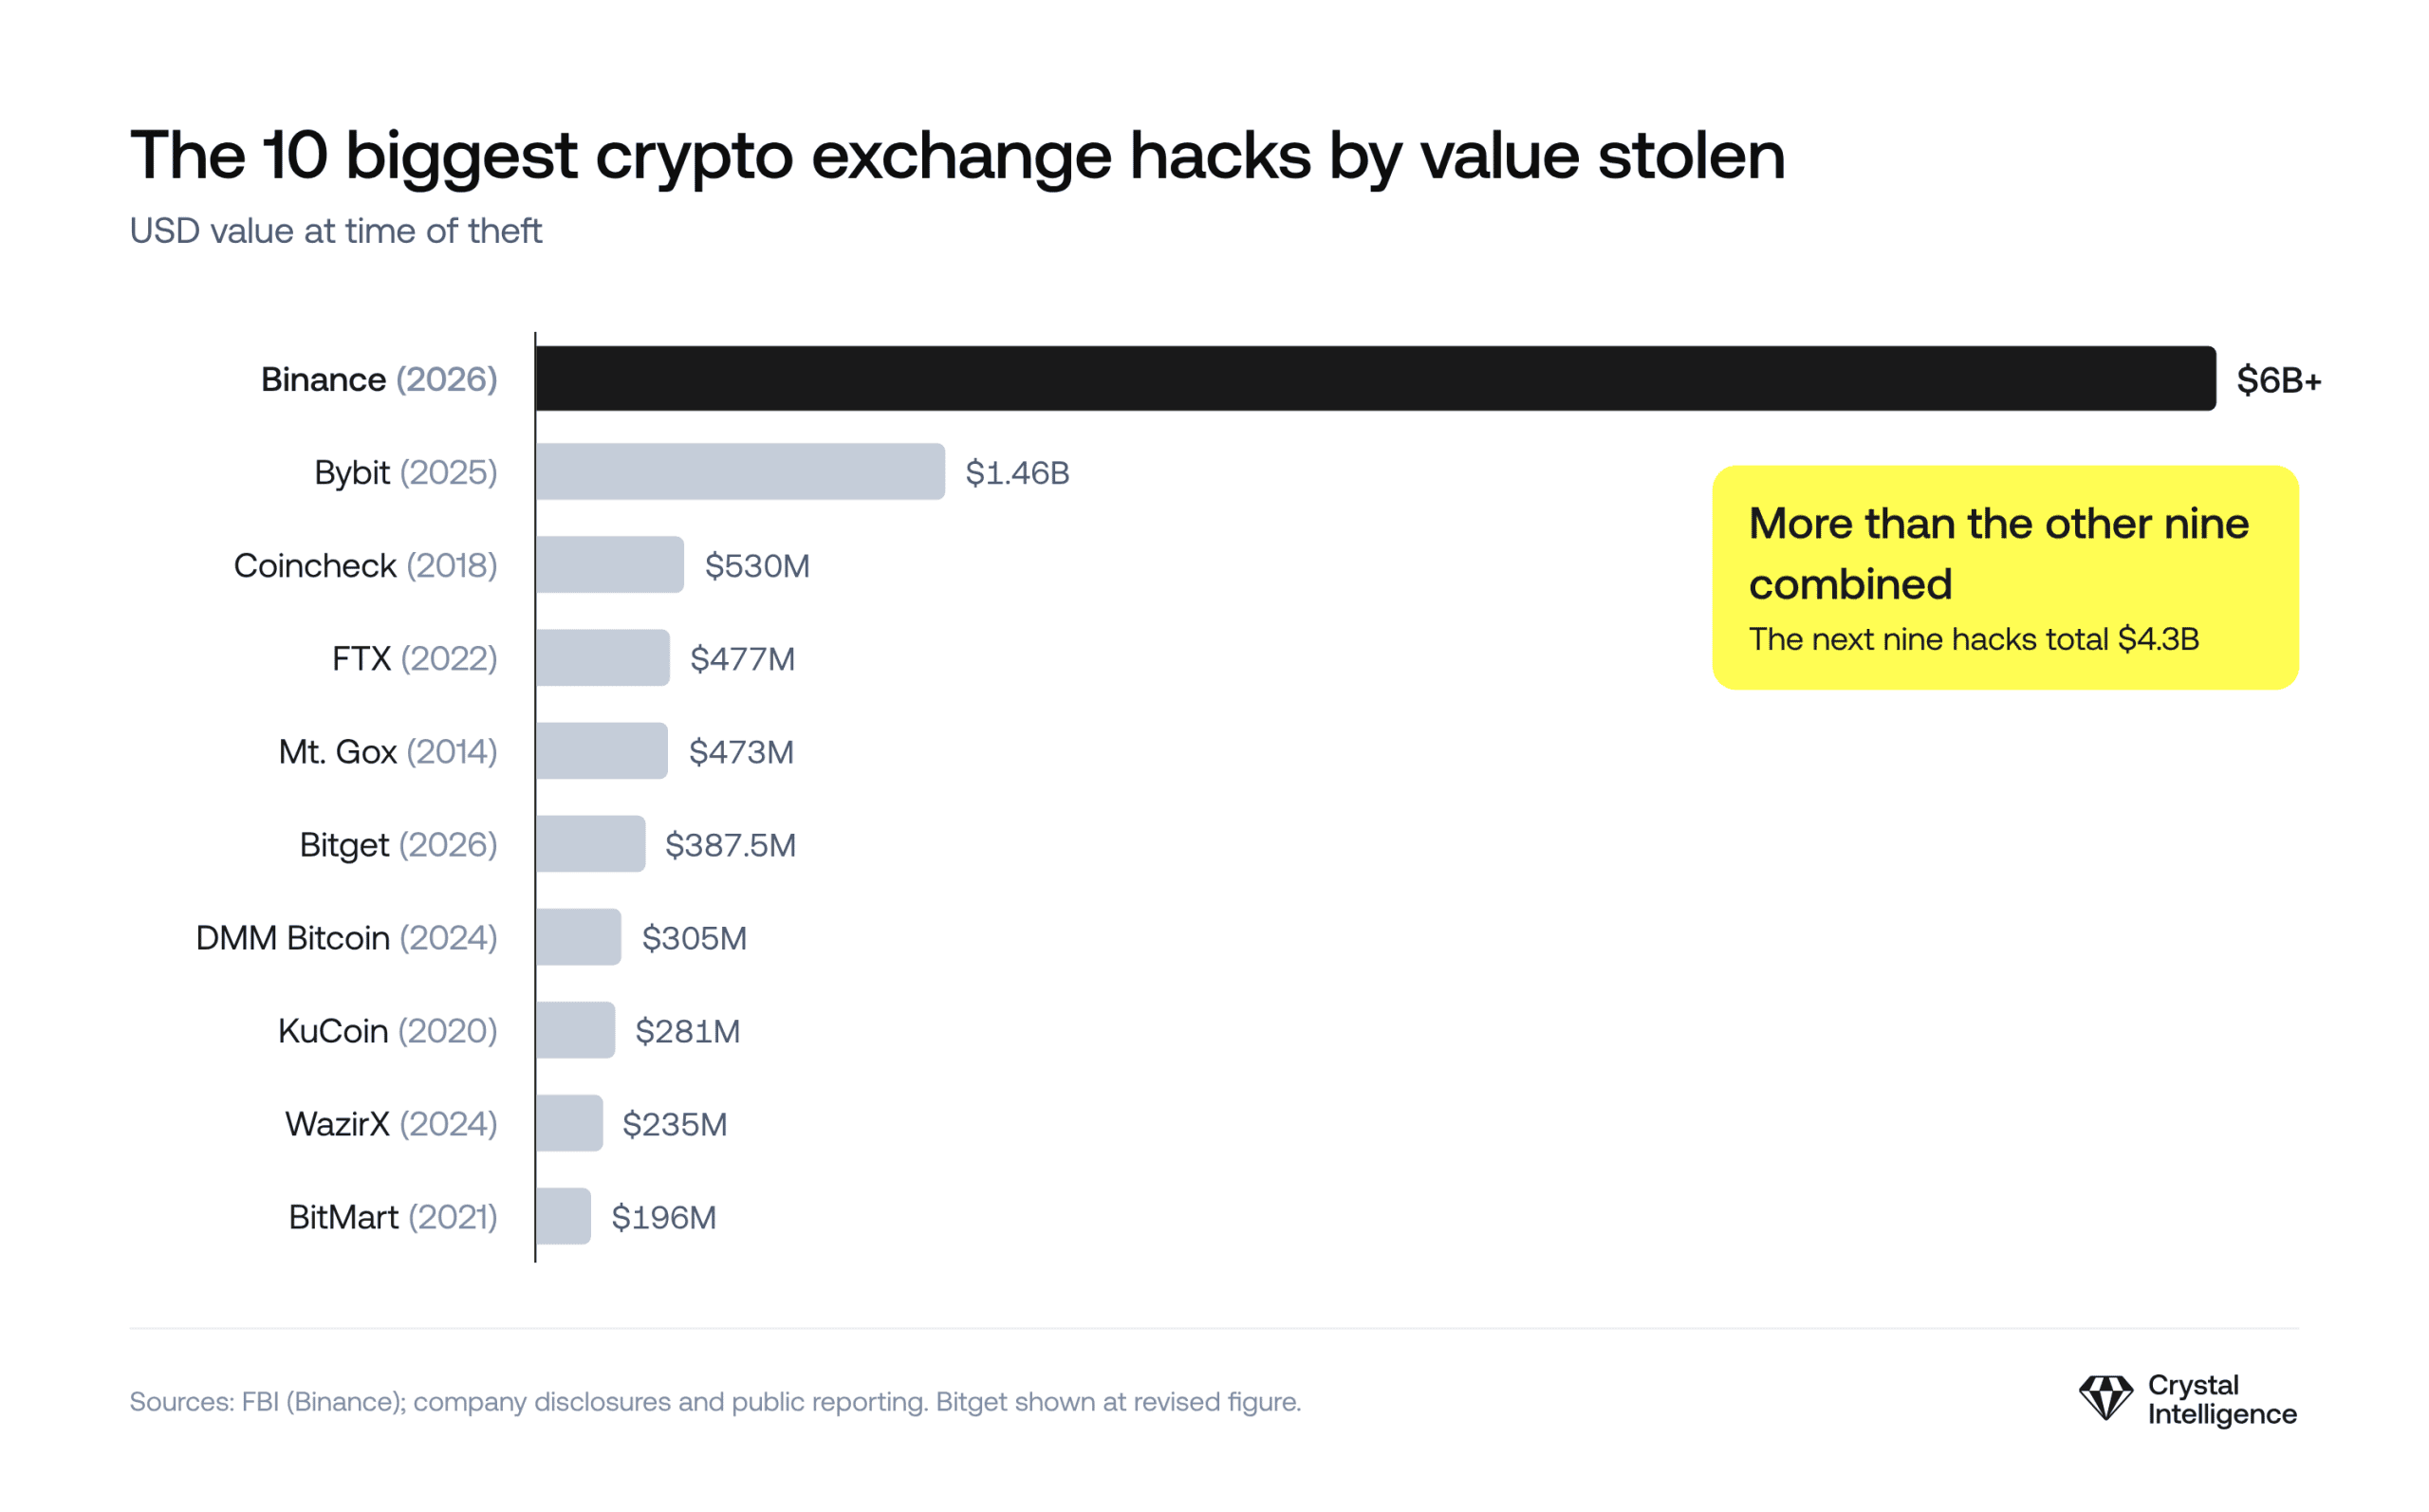
Above: Chart showing the enormity of the Binance attack, which alone constitutes about 60% of dollar value among the top 10 CEX hacks of all time. Source: Crystal Intelligence.
Key Takeaways
- Binance’s October 2026 loss of more than $6B is the largest crypto theft on record. It exceeds the other nine hacks on this list combined, which total about $4.3B.
- North Korean groups are confirmed or suspected in six of the 10 biggest exchange hacks. The FBI has attributed Binance, Bybit, and DMM Bitcoin to the same unit, TraderTraitor.
- Attackers now target the people and systems around private keys, not just the keys themselves. Binance, Bybit, WazirX, and DMM Bitcoin were hit through signing systems, wallet interfaces, or staff.
- Fast, coordinated action limits losses. Stablecoin issuers froze about $3B within hours of the Binance hack, and KuCoin recovered 84% of its stolen funds within weeks.
1. Binance: more than $6B stolen in 2026 hack
On October 29, 2026, Binance suffered the largest crypto theft on record. Starting at 20:20 UTC, wallets attributed to the exchange sent billions of dollars in assets out on Bitcoin, Ethereum, Tron, Solana, XRP, and other chains. On October 31, the FBI stated that North Korea was responsible for the theft of more than $6B in virtual assets. The FBI attributes this activity tothe Lazarus Group-linked TraderTraitor.
No smart contract was exploited. As we explain in Binance hack: what we know and what teams should do now, the attacker used EIP-7702, an Ethereum feature that lets a wallet delegate control to smart contract code. The delegation carried 50 pre-signed authorizations, and only one was valid. This points to compromised signing access, not a stolen private key. Binance’s preliminary findings agree: a possibly compromised DevOps engineer’s laptop may have granted access to a service container used to make the withdrawals*.
The response was fast. Tether and Circle froze large stablecoin balances within about an hour, and Binance put the frozen total at about $3B. The exchange quickly assured users it would cover all losses.
Binance lost more than the other nine exchanges on this list combined. The FBI expects the attackers to launder the remaining funds through DeFi and instant swap services. It has urged VASPs and blockchain analytics firms to block transactions linked to the addresses it published.
For compliance teams, the lesson is about signing policy. A signer that cannot decode what it approves can hand over a wallet without moving a single coin.
*This is an evolving story. Crystal will continue to update the reported causes of the exploit as verifiable information becomes available.
2. Bybit: $1.46B in ETH stolen in 2025 hack
On February 21, 2025, Dubai-based Bybit lost about 400,000 ETH, worth $1.46B, in what was then the largest crypto theft in history. As we set out in our breakdown of the Bybit exchange hack, attackers manipulated Bybit into approving a transaction that gave them control of a multisig cold wallet. In effect, they replaced Bybit’s vault keys with their own, giving them free access to its funds.
The attack began at 14:15 UTC on a Friday, as the UAE working day ended. A 90 USDT test transaction came first. One minute later, 401,347 ETH, 90,375 stETH, 15,000 cmETH, and 8,000 mETH left the wallet. Within 14 minutes, the attackers were swapping tokens for ETH through DeFi services and splitting funds across addresses.
Bybit confirmed the attack on X at 15:51 UTC and asked the industry for help. The next day, CEO Ben Zhou launched a bounty of up to 10%, or about $140M, for help recovering the funds. On February 26, the FBI attributed the theft to North Korea’sTraderTraitor.
The response set a new standard for cooperation between exchanges, analytics firms, and law enforcement. Our breakdown of how the hackers took control covers what exchanges can learn from it.
3. Coincheck: $534M in NEM stolen in 2018 hack
In January 2018, attackers stole about 523 million NEM (XEM) tokens, worth $534M, from Tokyo-based Coincheck, then the largest crypto theft ever. Phishing emails planted malware on employees’ computers, giving hackers access to the private key of a hot wallet that held almost all of the exchange’s NEM. Coincheck later repaid customers in yen, and Japan tightened its rules on exchange security.
4. FTX: $477M drained in 2022 post-collapse hack
On November 11, 2022, the day FTX filed for bankruptcy, about $477M in cryptowas transferred from its wallets in unauthorized transfers. Because the theft happened during the exchange’s collapse, some analysts treat it separately from conventional hacks. In 2024, US prosecutors charged three people over a SIM-swap scheme reportedly linked to the theft. Founder Sam Bankman-Fried is serving a 25-year sentence.
5. Mt. Gox: $460M in bitcoin lost by 2014
At its peak, Tokyo-based Mt. Gox handled most of the world’s bitcoin trading. In February 2014, it filed for bankruptcy, saying about 850,000 BTC, worth $460M at the time, was missing. Hackers had been draining its hot wallet since 2011, and weak security hid the losses. About 200,000 BTC was later found, and repayments began in 2024.
6. Bitget: $387.5M stolen in 2026 hack
On September 24, 2026, Bitget detected unauthorized transfers from several hot wallets. It initially put the loss at $351.6M, then revised it to $387.5M after accounting for assets on Zcash and Tron. Attackers used a flaw in a third-party security product to obtain internal credentials and send fake withdrawal commands. Bitget suspects a North Korean group and says its User Protection Fund covers the loss.
7. DMM Bitcoin: $308M in bitcoin stolen in 2024 hack
On May 31, 2024, Japan’s DMM Bitcoin lost 4,502.9 BTC, worth about $308M. The FBI and Japanese police later attributed the theft to TraderTraitor. They said the attackers posed as a LinkedIn recruiter and sent a malicious coding test to an employee at Ginco, DMM’s wallet software provider. DMM could not recover and moved its accounts to SBI VC Trade in 2025.
8. KuCoin: $281M stolen in 2020 hack
In September 2020, attackers obtained the private keys to KuCoin’s hot wallets and stole about $281M in crypto. KuCoin worked with token projects, other exchanges, and analytics firms to freeze and trace the funds, and recovered about 84%, more than $204M, within weeks. Investigators later linked the attack to North Korea’s Lazarus Group.
9. WazirX: $235M stolen in 2024 hack
On July 18, 2024, India’sWazirX lost about $235M from a multisig wallet. Signers approved a transaction that differed from what their interface showed, handing control of the wallet to the attacker. The theft has been linked to North Korea’s Lazarus Group, and the method matched that used in the later Bybit attack. Read ourexpert analysis of the WazirX hack.
10. BitMart: $196M stolen in 2021 hack
In December 2021, attackers used a stolen private key to drain two BitMart hot wallets, taking about $196M across Ethereum and BNB Smart Chain. They swapped the tokens through decentralized exchanges and used Tornado Cash to hide the trail. BitMart, which put its own loss at $150M, covered affected users from company funds.
The 2026 Coldcard exploit: $130M stolen from self-custody wallets
Every hack above targeted an exchange. The Coldcard exploit did not. On July 30, 2026, attackers drained 1,196 bitcoin addresses in 41 minutes. Galaxy Research has since verified 1,596 BTC stolen from about 7,300 addresses across three waves, and a suspected fourth wave could take the total to around 2,055 BTC, or $130M. The cause was a 2021 firmware change that left Mk3 devices with about 40 bits of entropy instead of 128. Attackers guessed the seed phrases and rebuilt the private keys without touching the devices.
As of August 7, 2026, around 90% of the stolen bitcoin had not moved. We followed the on-chain trail in tracing the Coldcard hack: where the stolen bitcoin went.
Frequently asked questions
What is the biggest crypto hack in history?
The October 29, 2026, Binance hack is the largest on record. The FBI attributed the theft of more than $6B in virtual assets to North Korea’s TraderTraitor unit. It surpassed the $1.46B Bybit hack of February 2025.
How do hackers steal crypto from exchanges?
Most attacks target hot wallets or the systems that approve withdrawals. Attackers steal private keys, compromise signing services, trick staff with phishing or fake job offers, or manipulate the interface signers use to approve transactions, as at Bybit and WazirX.
Can stolen crypto be recovered?
Sometimes. Stablecoin issuers can freeze tokens, as Tether and Circle did within hours of the Binance hack, and fast tracing helped KuCoin recover 84% of its stolen funds. Once assets move through DeFi swaps or mixers, recovery becomes much harder.
How can exchanges protect themselves from hacks?
Exchanges should use signing policies that decode every transaction before approval, keep most funds in cold storage, and train staff to spot social engineering. Real-time transaction monitoring and shared intelligence on attacker wallets help teams freeze and trace funds quickly.
What do the biggest crypto hacks reveal about exchange security?
Half of the 10 largest exchange hacks have occurred since May 2024, and the two largest have taken place in the past 20 months. Attacks are getting bigger, more frequent, and better organized, with state-backed groups behind the largest losses.
The methods have changed too. Early attacks, such as those on Mt. Gox and Coincheck, stole keys from poorly protected hot wallets. Recent attacks target the people and systems around the keys: the signing service at Binance, the wallet interface at Bybit and WazirX, and an employee at a wallet provider for DMM Bitcoin.
The industry response is also getting stronger and faster. Stablecoin issuers froze about $3B within hours of the Binance hack, and the FBI published attacker addresses within two days. But freezes only work when the whole industry acts on the same data in real-time. Exchanges need signing policies that decode what they approve, real-time transaction monitoring, and fast access to verified, shared intelligence on attacker wallets as funds move.